(217) Microsoft Intune - App Protection Policies

Been working with a customer who wants to implement MAM within their tenant, as far as we know that Microsoft made the change a few years ago where Target to apps on all device types can no longer by default change to No, by default if you were to create a new App protection policy it will be yes.
The two personas that will be targeted are:
Personal Android and iOS/iPadOS
Corporate Android and iOS/iPadOS
We will need to create filters for this to work, MAM (App Protection Policies) can only be applied to users (not devices) as we have to take consideration users who have a BYOD (personal) which isn't managed by Intune.
Navigate to https://intune.microsoft.com/ then select Devices then select Assignment filters then select Create then select Managed apps.

Android Apps Managed
Rule syntax:
(app.deviceManagementType -eq "Corporate-owned fully managed") or (app.deviceManagementType -eq "Corporate-owned with work profile") or (app.deviceManagementType -eq "Personally-owned work profile")
Android Apps Unmanaged Rule syntax:
(app.deviceManagementType -eq "Unmanaged") iOS Apps Unmanaged
Rule syntax:
(app.deviceManagementType -eq "Unmanaged")
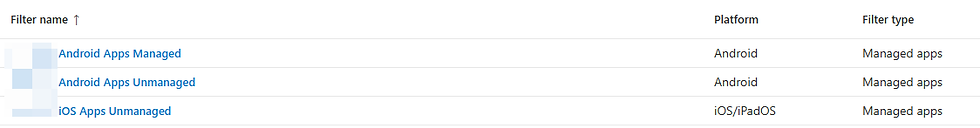
Once done, it will look like this:
For Personal Android App Protection Policy, the setup is as follows: Basics
Setting | Value |
Name | Android - Personal Application Protection |
Description | No Description |
Platform | Android |
Apps
Setting | Value |
Target to apps on all device types | Yes |
Device types | No Device types |
Public apps | Core Microsoft Apps |
Custom apps | No Custom apps |
Data Protection
Setting | Value |
Prevent backups | Block |
Send org data to other apps | Policy managed apps |
Select apps to exempt | No Select apps to exempt |
Save copies of org data | Block |
Allow user to save copies to selected services | OneDrive for Business, SharePoint |
Transfer telecommunication data to | Any dialer app |
Dialer App Package ID | No Dialer App Package ID |
Dialer App Name | No Dialer App Name |
Transfer messaging data to | Any messaging app |
Messaging App Package ID | No Messaging App Package ID |
Messaging App Name | No Messaging App Name |
Receive data from other apps | All Apps |
Open data into Org documents | Block |
Allow users to open data from selected services | OneDrive for Business, SharePoint, Camera, Photo Library |
Restrict cut, copy, and paste between other apps | Policy managed apps with paste in |
Cut and copy character limit for any app | 0 |
Screen capture and Google Assistant | Disable |
Approved keyboards | Not required |
Select keyboards to approve | No Select keyboards to approve |
Encrypt org data | Require |
Encrypt org data on enrolled devices | Require |
Sync policy managed app data with native apps or add-ins | Allow |
Printing org data | Block |
Restrict web content transfer with other apps | Microsoft Edge |
Unmanaged Browser ID | No Unmanaged Browser ID |
Unmanaged Browser Name | No Unmanaged Browser Name |
Org data notifications | Allow |
Start Microsoft Tunnel connection on app-launch | No |
Access Requirements
Setting | Value |
PIN for access | Require |
PIN type | Numeric |
Simple PIN | Block |
Select minimum PIN length | 6 |
Biometrics instead of PIN for access | Allow |
Override biometrics with PIN after timeout | Require |
Timeout (minutes of inactivity) | 720 |
Class 3 Biometrics (Android 9.0+) | Require |
Override Biometrics with PIN after biometric updates | Not required |
PIN reset after number of days | Yes |
Number of days | 720 |
Select number of previous PIN values to maintain | 0 |
App PIN when device PIN is set | Require |
Work or school account credentials for access | Not required |
Recheck the access requirements after (minutes of inactivity) | 30 |
Conditional Launch
Setting | Value | Action |
Max PIN attempts | 5 | Reset PIN |
Offline grace period | 10080 (minutes) | Block access |
Offline grace period | 30 (days) | Wipe data |
Disabled account | — | Block access |
Jailbroken/rooted devices | — | Block access |
Min OS version | 9.0 | Block access |
Play integrity verdict | Basic integrity and device integrity | Block access |
Require threat scan on apps | — | Block access |
Play Integrity verdict evaluation type | Check strong integrity | — |
Require device lock | Medium Complexity | Block access |
Assignments
Included Groups
Group | Status | Filter | Filter Mode |
Test User Group | Active | Android Apps Unmanaged | Include |
For Corporate Android App Protection policy, the setup is as follows: Basics
Setting | Value |
Name | Android - Corporate Application Protection |
Description | No Description |
Platform | Android |
Apps
Setting | Value |
Target to apps on all device types | No Device types |
Public apps | Core Microsoft Apps |
Custom apps | No Custom apps |
Data Protection
Setting | Value |
Prevent backups | Block |
Send org data to other apps | Policy managed apps |
Select apps to exempt | No Select apps to exempt |
Save copies of org data | Allow |
Allow user to save copies to selected services | OneDrive for Business, SharePoint |
Transfer telecommunication data to | Any dialer app |
Dialer App Package ID | No Dialer App Package ID |
Dialer App Name | No Dialer App Name |
Transfer messaging data to | Any messaging app |
Messaging App Package ID | No Messaging App Package ID |
Messaging App Name | No Messaging App Name |
Receive data from other apps | All Apps |
Open data into Org documents | Allow |
Allow users to open data from selected services | OneDrive for Business, SharePoint, Camera, Photo Library |
Restrict cut, copy, and paste between other apps | Policy managed apps with paste in |
Cut and copy character limit for any app | 0 |
Screen capture and Google Assistant | Enable |
Approved keyboards | Not required |
Select keyboards to approve | No Select keyboards to approve |
Encrypt org data | Require |
Encrypt org data on enrolled devices | Require |
Sync policy managed app data with native apps or add-ins | Allow |
Printing org data | Allow |
Restrict web content transfer with other apps | Microsoft Edge |
Unmanaged Browser ID | No Unmanaged Browser ID |
Unmanaged Browser Name | No Unmanaged Browser Name |
Org data notifications | Allow |
Start Microsoft Tunnel connection on app-launch | No |
Access Requirements
Setting | Value |
PIN for access | Require |
PIN type | Numeric |
Simple PIN | Block |
Select minimum PIN length | 6 |
Biometrics instead of PIN for access | Allow |
Override biometrics with PIN after timeout | Require |
Timeout (minutes of inactivity) | 720 |
Class 3 Biometrics (Android 9.0+) | Require |
Override Biometrics with PIN after biometric updates | Not required |
PIN reset after number of days | Yes |
Number of days | 720 |
Select number of previous PIN values to maintain | 0 |
App PIN when device PIN is set | Require |
Work or school account credentials for access | Not required |
Recheck the access requirements after (minutes of inactivity) | 60 |
Conditional Launch
Setting | Value | Action |
Max PIN attempts | 5 | Reset PIN |
Offline grace period | 10080 (minutes) | Block access |
Offline grace period | 30 (days) | Wipe data |
Disabled account | — | Block access |
Jailbroken/rooted devices | — | Block access |
Play integrity verdict | Basic integrity and device integrity | Block access |
Require threat scan on apps | — | Block access |
Play Integrity verdict evaluation type | Check strong integrity | — |
Require device lock | Medium Complexity | Block access |
Assignments
Included Groups
Group | Status | Filter | Filter Mode |
Test User Group | Active | Android Apps Managed | Include |
For Personal iOS App Protection Policy, the setup is as follows:
Basics
Setting | Value |
Name | iOS/iPadOS - Personal Application Protection |
Description | No Description |
Platform | iOS/iPadOS |
Apps
Setting | Value |
Target to apps on all device types | Yes |
Device types | No Device types |
Public apps | Core Microsoft Apps |
Custom apps | No Custom apps |
Data Protection
Setting | Value |
Prevent backups | Block |
Send org data to other apps | Policy managed apps with Open-In/Share filtering |
Select apps to exempt | — |
Select universal links to exempt | Default (Apple, Microsoft, Skype, Teams, Zoom, ServiceNow links) |
Save copies of org data | Block |
Allow user to save copies to selected services | OneDrive for Business, SharePoint |
Transfer telecommunication data to | Any dialer app |
Dialer App URL Scheme | No Dialer App URL Scheme |
Transfer messaging data to | Any messaging app |
Messaging App URL Scheme | No Messaging App URL Scheme |
Receive data from other apps | All Apps |
Open data into Org documents | Allow |
Allow users to open data from selected services | OneDrive for Business, SharePoint, Camera |
Restrict cut, copy, and paste between other apps | Policy managed apps with paste in |
Cut and copy character limit for any app | 0 |
Third party keyboards | Block |
Encrypt org data | Require |
Sync policy managed app data with native apps or add-ins | Allow |
Printing org data | Allow |
Restrict web content transfer with other apps | Microsoft Edge |
Unmanaged browser protocol | No Unmanaged browser protocol |
Org data notifications | Allow |
Genmoji | Block |
Screen capture | Block |
Writing tools | Block |
Access Requirements
Setting | Value |
PIN for access | Require |
PIN type | Numeric |
Simple PIN | Block |
Select minimum PIN length | 6 |
Touch ID instead of PIN for access (iOS 8+/iPadOS) | Allow |
Override biometrics with PIN after timeout | Require |
Timeout (minutes of inactivity) | 720 |
Face ID instead of PIN for access (iOS 11+/iPadOS) | Allow |
PIN reset after number of days | Yes |
Number of days | 730 |
App PIN when device PIN is set | Require |
Work or school account credentials for access | Not required |
Recheck the access requirements after (minutes of inactivity) | 30 |
Conditional Launch
Setting | Value | Action |
Max PIN attempts | 5 | Reset PIN |
Offline grace period | 10080 (minutes) | Block access |
Offline grace period | 30 (days) | Wipe data |
Disabled account | — | Block access |
Jailbroken/rooted devices | — | Wipe data |
Min OS version | 15.0 | Block access |
Max allowed device threat level | Secured | Block access |
Assignments
Included Groups
Group | Status | Filter | Filter Mode |
Intune MAM Personal Pilot | Active | iOS Apps Unmanaged | Include |
For Corporate iOS App Protection Policy, the setup is as follows:
Basics
Setting | Value |
Name | iOS/iPadOS - Corporate Application Protection |
Description | No Description |
Platform | iOS/iPadOS |
Apps
Setting | Value |
Target to apps on all device types | Yes |
Device types | No Device types |
Public apps | Core Microsoft Apps |
Custom apps | No Custom apps |
Data Protection
Setting | Value |
Prevent backups | Block |
Send org data to other apps | All Apps |
Select apps to exempt | — |
Select universal links to exempt | Default (Apple, Microsoft, Skype, Teams, Zoom, ServiceNow links) |
Save copies of org data | Allow |
Allow user to save copies to selected services | OneDrive for Business, SharePoint |
Transfer telecommunication data to | Any dialer app |
Dialer App URL Scheme | No Dialer App URL Scheme |
Transfer messaging data to | Any messaging app |
Messaging App URL Scheme | No Messaging App URL Scheme |
Receive data from other apps | All Apps |
Open data into Org documents | Allow |
Allow users to open data from selected services | OneDrive for Business, SharePoint, Camera, Photo Library |
Restrict cut, copy, and paste between other apps | Policy managed apps with paste in |
Cut and copy character limit for any app | 0 |
Third party keyboards | Block |
Encrypt org data | Require |
Sync policy managed app data with native apps or add-ins | Allow |
Printing org data | Allow |
Restrict web content transfer with other apps | Microsoft Edge |
Unmanaged browser protocol | No Unmanaged browser protocol |
Org data notifications | Allow |
Genmoji | Block |
Screen capture | Block |
Writing tools | Block |
Access Requirements
Setting | Value |
PIN for access | Require |
PIN type | Numeric |
Simple PIN | Block |
Select minimum PIN length | 6 |
Touch ID instead of PIN for access (iOS 8+/iPadOS) | Allow |
Override biometrics with PIN after timeout | Not required |
Timeout (minutes of inactivity) | 0 |
Face ID instead of PIN for access (iOS 11+/iPadOS) | Allow |
PIN reset after number of days | No |
Number of days | 0 |
App PIN when device PIN is set | Require |
Work or school account credentials for access | Not required |
Recheck the access requirements after (minutes of inactivity) | 60 |
Conditional Launch
Setting | Value | Action |
Max PIN attempts | 5 | Reset PIN |
Offline grace period | 10080 (minutes) | Block access |
Offline grace period | 30 (days) | Wipe data |
Disabled account | — | Block access |
Jailbroken/rooted devices | — | Block access |
Min OS version | 15.0 | Block access |
Max allowed device threat level | Secured | Block access |
Assignments
Included Groups
Group | Status | Filter | Filter Mode |
Test User Group | Active | iOS Apps Unmanaged | Exclude |
With this setup in place, you can track the progress by adding yourself or other users into the test groups where the filters will do the searching, and correctly apply the MAM policies based on the policy.


Comments